

Welcome to the first Scenario Clinic!
When I was preparing for the CISSP, and earlier, when I was new to the field, there was one thing I kept missing.
There was no shortage of material. Books, videos, practice tests, flashcards. I could explain almost every concept.
And I still lost points on the questions where two or three answers all looked right.
What I was missing wasn’t more knowledge. It was the mindset: how a security professional thinks through a situation and decides what comes first. And almost nobody explained that. Practice tests told me which answer was correct, but rarely why the others were wrong.
That’s what this clinic is for.
Every week, I take the topic of the free article and turn it into exam-style scenarios, with the reasoning behind every option. Because once you understand how to think about a scenario, the right answer gets much easier to find, on the exam and in a real incident.
This week’s topic: the $6.3 billion Binance hack. If you haven’t read the free article yet, start here: The $6.3 Billion Binance Hack, Explained in Plain English
How to use this clinic:
Read all three scenarios.
Write down your answer for each one before scrolling.
Then check the explanations. The wrong options matter as much as the right one.
Why this is the fastest way to improve
Most people study by reading more. But reading only teaches you to recognize the right answer once you see it.
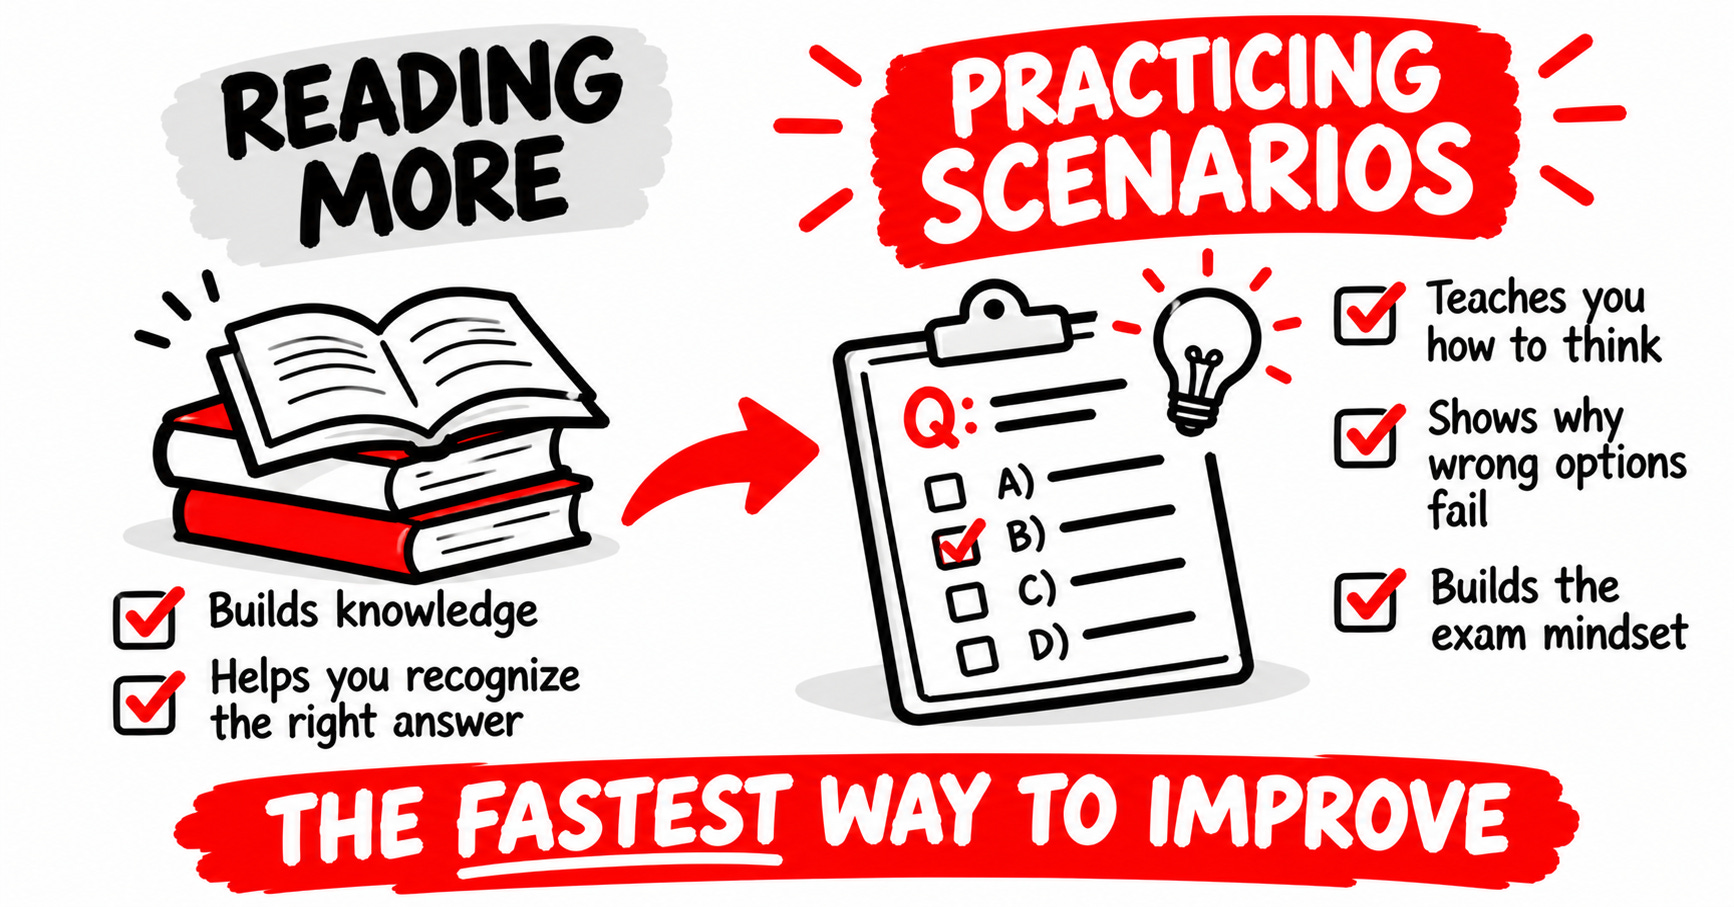
The exam, and the job, ask for something else: picking the best option when several look reasonable.
That’s why every scenario here explains why each wrong option fails, not just which one is right. The wrong options are where you learn the most. They show you the traps the exam sets, and the shortcuts people take in real incidents.
Do this every week, and you’ll start seeing the patterns!
Scenario 1: The engineer’s laptop
CC Domain 3: Identity and Access Management
A DevOps engineer uses the same laptop for email, web browsing and administering the production service that submits customer withdrawals. The security team wants to reduce the risk that a compromised laptop leads to access to production.
What is the BEST control?
A) Install a stronger antivirus product on the laptop
B) Require privileged tasks to be done from a dedicated, hardened admin workstation, using a separate admin account
C) Require the engineer to change their password every 30 days
D) Block social media websites on the laptop
